
Industrial equipment is built to perform under pressure, but rarely to withstand a cyberattack.
In facilities across Qatar’s energy, utilities, and manufacturing sectors, many machines still run on control networks designed decades ago. Duplicate addressing, default logins, and controllers that accept commands from any connected device were never considered a risk while these systems stayed isolated. Today the same machines feed data into operations centers, accept remote maintenance sessions, and share infrastructure with corporate IT. Each new link widens the path to equipment that cannot protect itself.
Operators want real-time machine data without putting uptime at risk, and national cybersecurity requirements in Qatar are pushing critical infrastructure operators toward stronger OT protection. For system integrators and machine builders delivering projects in Qatar, demonstrating how equipment is secured is quickly becoming part of the tender.
How to respond depends on the stage a machine has reached. For equipment already installed, protection belongs at the edge of its network, so operation continues exactly as before. For equipment still in design, protection can be built into each networked device. This guide explains both routes using Moxa solutions available from Rockford Communication Solutions, Moxa’s partner in Qatar.
 Machines in service
Need to Harden Machines Already in the Field?
Protecting equipment that is already running calls for a light-touch approach. Add security layers without editing PLC logic and without pausing production.
 New machine designs
Planning a Machine From the Ground Up?
When you are engineering a new machine, specify secure-by-design components early so cybersecurity becomes part of the architecture instead of an afterthought.
RETROFIT SECURITY FOR EXISTING MACHINES
Retrofit Legacy Machines Without Rewriting PLC Programs
The PLC is the brain of any machine, which is why a security upgrade must never compete with it. Plug-and-play, zero-configuration protection keeps legacy assets safe while network behavior and PLC programs stay exactly as they are.
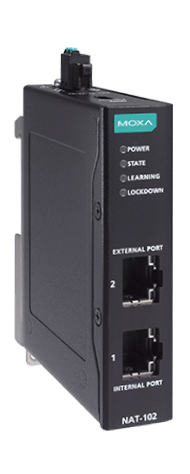
NAT-102 Series
Compact 2-port industrial Network Address Translation (NAT) device
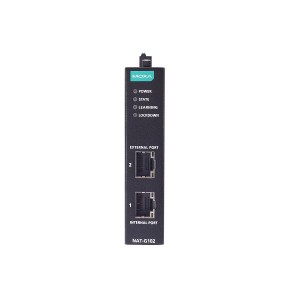
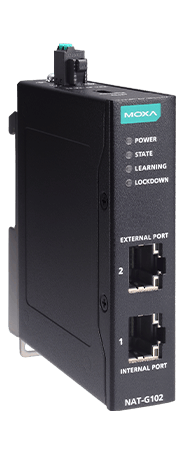
NAT-G102 Series
2-port industrial Network Address Translation (NAT) device with Gigabit Ethernet ports
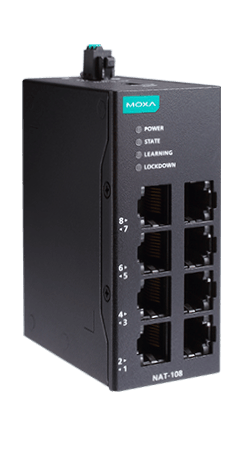
NAT-108 Series
8-port industrial Network Address Translation (NAT) device
Industrial NAT Devices
NAT-(G)102 / NAT-108 Series
With 1:1 NAT mapping, the NAT-(G)102 and NAT-108 Series resolve overlapping IP addresses, so machines can be introduced to the plant network in a controlled and repeatable way.

Simple IP Address Handling

Automatic Network Access Control

Slim, DIN-Rail-Friendly Size
Industrial LAN Firewalls
EDF-G1002-BP Series
Designed with OEMs in mind, the EDF-G1002-BP Series adds cyber-resilience to machines while keeping integration effortless and uptime intact.

Transparent Filtering Mode

Industrial DPI Technology

IPS and DoS Protection
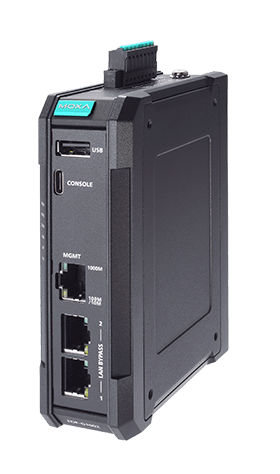
EDF-G1002-BP Series
Next-generation industrial LAN firewall with 2 Gigabit ports
SECURITY BY DESIGN FOR NEW MACHINES
Engineer Cyber-resilient Machines From the First Schematic
Specifying protected components at the cabinet-design stage closes security gaps early, makes audits easier, and supports regulatory compliance.
Security Designed In, Not Added Later
Every Moxa product follows an IEC 62443-4-1 ML3 certified process, giving you hardened hardware and software that integrate cleanly from the very start.
Quicker Supply Chain Sign-off
Shorten vendor approval cycles with complete SBOM management, security guides, and a direct line to the Product Security Incident Response Team (PSIRT).
Everyday Protection on the Plant Floor
Role-based access control (RBAC), network access control, and event logs make it easier to oversee and defend machines during daily operation.
Availability You Can Plan Around
Under Moxa's Product Life-cycle Management Policy, components stay available and security patches keep coming for years, so you avoid costly machine redesigns.
SOLUTION PORTFOLIO
Secure-by-design Devices for Edge Connectivity
NPort 6000-G2 Series
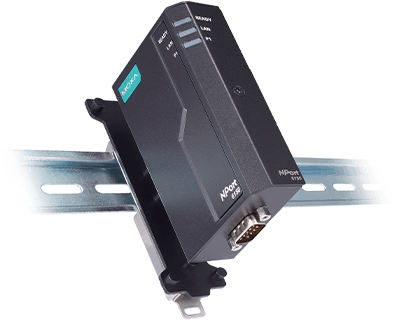
Serial device servers with robust access control for protected serial-to-Ethernet connectivity.
- Achieves IEC 62443-4-2 Security Level 2 certification
- Centralized authentication and remote syslog ease integration with IT systems
- RBAC and syslog event logging, plus safeguards for serial data and management interfaces
MGate MB3170-G2/MB3270-G2/MB3470-G2 Series
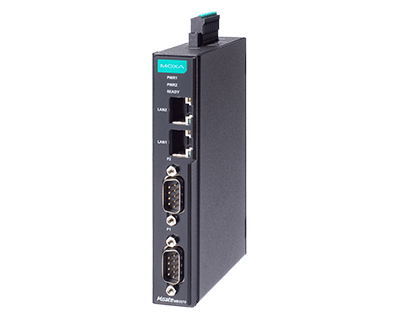
Modbus gateways with a high-performance agent mode and strengthened security.
- Satisfies IEC 62443-4-2 Security Level 2 requirements
- Detailed traffic logging and audit trails
- Secure boot loader in hardware guards against firmware tampering
ioLogik 1400 Series
*Preliminary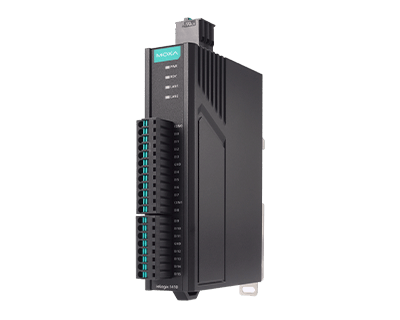
Next-generation standalone Ethernet remote I/O with security included.
- Conforms to IEC 62443-4-2 Security Level 2 requirements
- RSTP keeps Ethernet networks resilient
- Push-in terminal blocks for quicker wiring
*Scheduled for release in December 2026.
SDS-(G)3000 Series
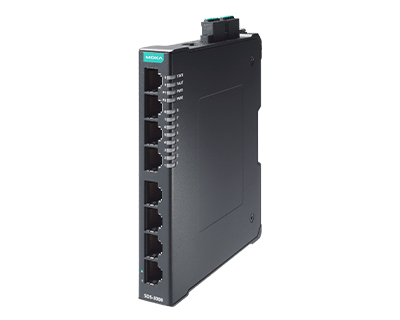
Ultra-compact smart switches that protect the machine network and connect easily to PLCs.
- Trusted access control preserves machine network integrity
- EtherNet/IP, PROFINET, and Modbus TCP support for straightforward PLC integration
- Tiny footprint suits crowded control panels
Where Machine Security Makes a Difference: Real Industrial Use Cases
Securing the Machine Perimeter Without Reprogramming PLCs
Engineering Secure-by-design Networks for Wind Turbine Systems
Few sites can choose just one route. Long-running equipment that must remain untouched usually shares the facility with upcoming expansions and new packages, so the most effective plan covers both under one security baseline. Starting with machines that have remote access or directly affect production keeps the first phase focused and measurable. Before contacting us, it helps to prepare the essentials: the machines involved, their current network connections, the protocols they rely on, and any security clauses in your project specifications or client requirements. The Rockford Communication Solutions team can then propose the right Moxa devices for each machine and support your project locally in Qatar, from selection to deployment.
Related Products